
If you are evaluating AI tools for HR or employee benefits, you have probably seen a vendor mention the NIST AI RMF. It tends to appear near the bottom of a security page, next to SOC 2 and HIPAA, and most buyers move past it without knowing what it means. That is a missed opportunity, because it is one of the more useful signals available about how seriously a vendor takes AI risk.
What the NIST AI RMF Is
The Artificial Intelligence Risk Management Framework, known as the AI RMF, was developed by the National Institute of Standards and Technology to help organizations identify, assess, and manage the risks that come with designing, developing, and using AI systems, and to build trustworthiness into those systems from the start. It is voluntary.
Unlike HIPAA, it is not a law. Unlike SOC 2, it does not produce an audit report. Organizations align to it, which means they structure their AI risk practices around its guidance.
The Four Functions
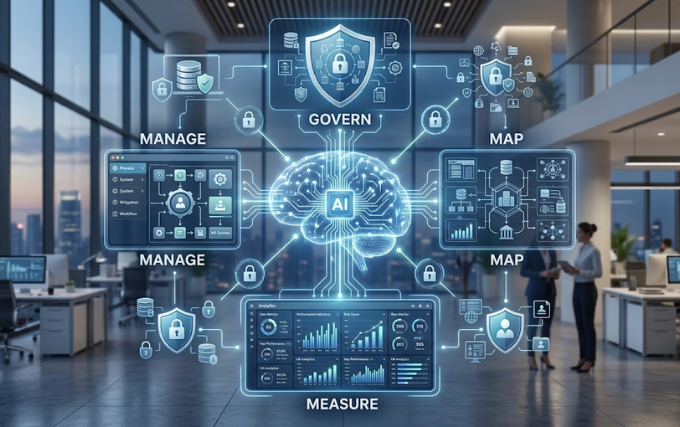
The framework is organized around four core functions that work together throughout the life of an AI system.
Govern establishes the culture, policies, and accountability structures that make risk management possible. It is where leadership commitment and clear ownership live.
Map puts an AI system in context: what it does, who it affects, and where its potential impacts lie.
Measure uses quantitative and qualitative methods to analyze, benchmark, and monitor those risks.
Manage allocates resources to address identified risks and sets out how the organization responds when something goes wrong.
These are not one time steps. NIST designed them to be applied continuously, which fits the reality that AI systems change as they are used.
A Framework That Keeps Evolving
NIST is actively building on this foundation. In December 2025, it released a preliminary draft of its Cyber AI Profile, which applies the NIST Cybersecurity Framework 2.0 to AI across three focus areas: securing AI systems, using AI to strengthen cyber defense, and thwarting AI enabled attacks. NIST positions the profile as a complement to the AI RMF, meant to be used alongside it. For buyers, that is a signal that AI governance and AI security are converging, and vendors aligned to the AI RMF are better positioned to keep up.
Why It Matters in Benefits
AI in benefits is no longer limited to answering questions. Platforms now analyze claims, model plan designs, and in agentic systems, take action on behalf of employers and employees. Those actions affect people’s money and care. A vendor aligned to the NIST AI RMF has, at a minimum, thought through who is accountable for those actions, how risks are measured, and what happens when the system gets something wrong.
When a vendor says it is aligned, ask how. Who owns AI governance? How are consequential decisions reviewed by a human? How is model behavior monitored? Is customer data ever used to train models?
Forsure is one vendor that builds this alignment into its platform. Its agentic AI operates within defined guardrails, with human accountability for consequential decisions, and its governance program is aligned to the NIST AI RMF alongside SOC 2, HIPAA, and TX-RAMP Level II. Forsure also does not use customer data to train foundation models.
The Bottom Line
The NIST AI RMF will not tell you whether an AI product is good. It will tell you whether the people behind it have a disciplined way of managing its risks. For anyone trusting AI with employee data, that is worth knowing before you sign.
